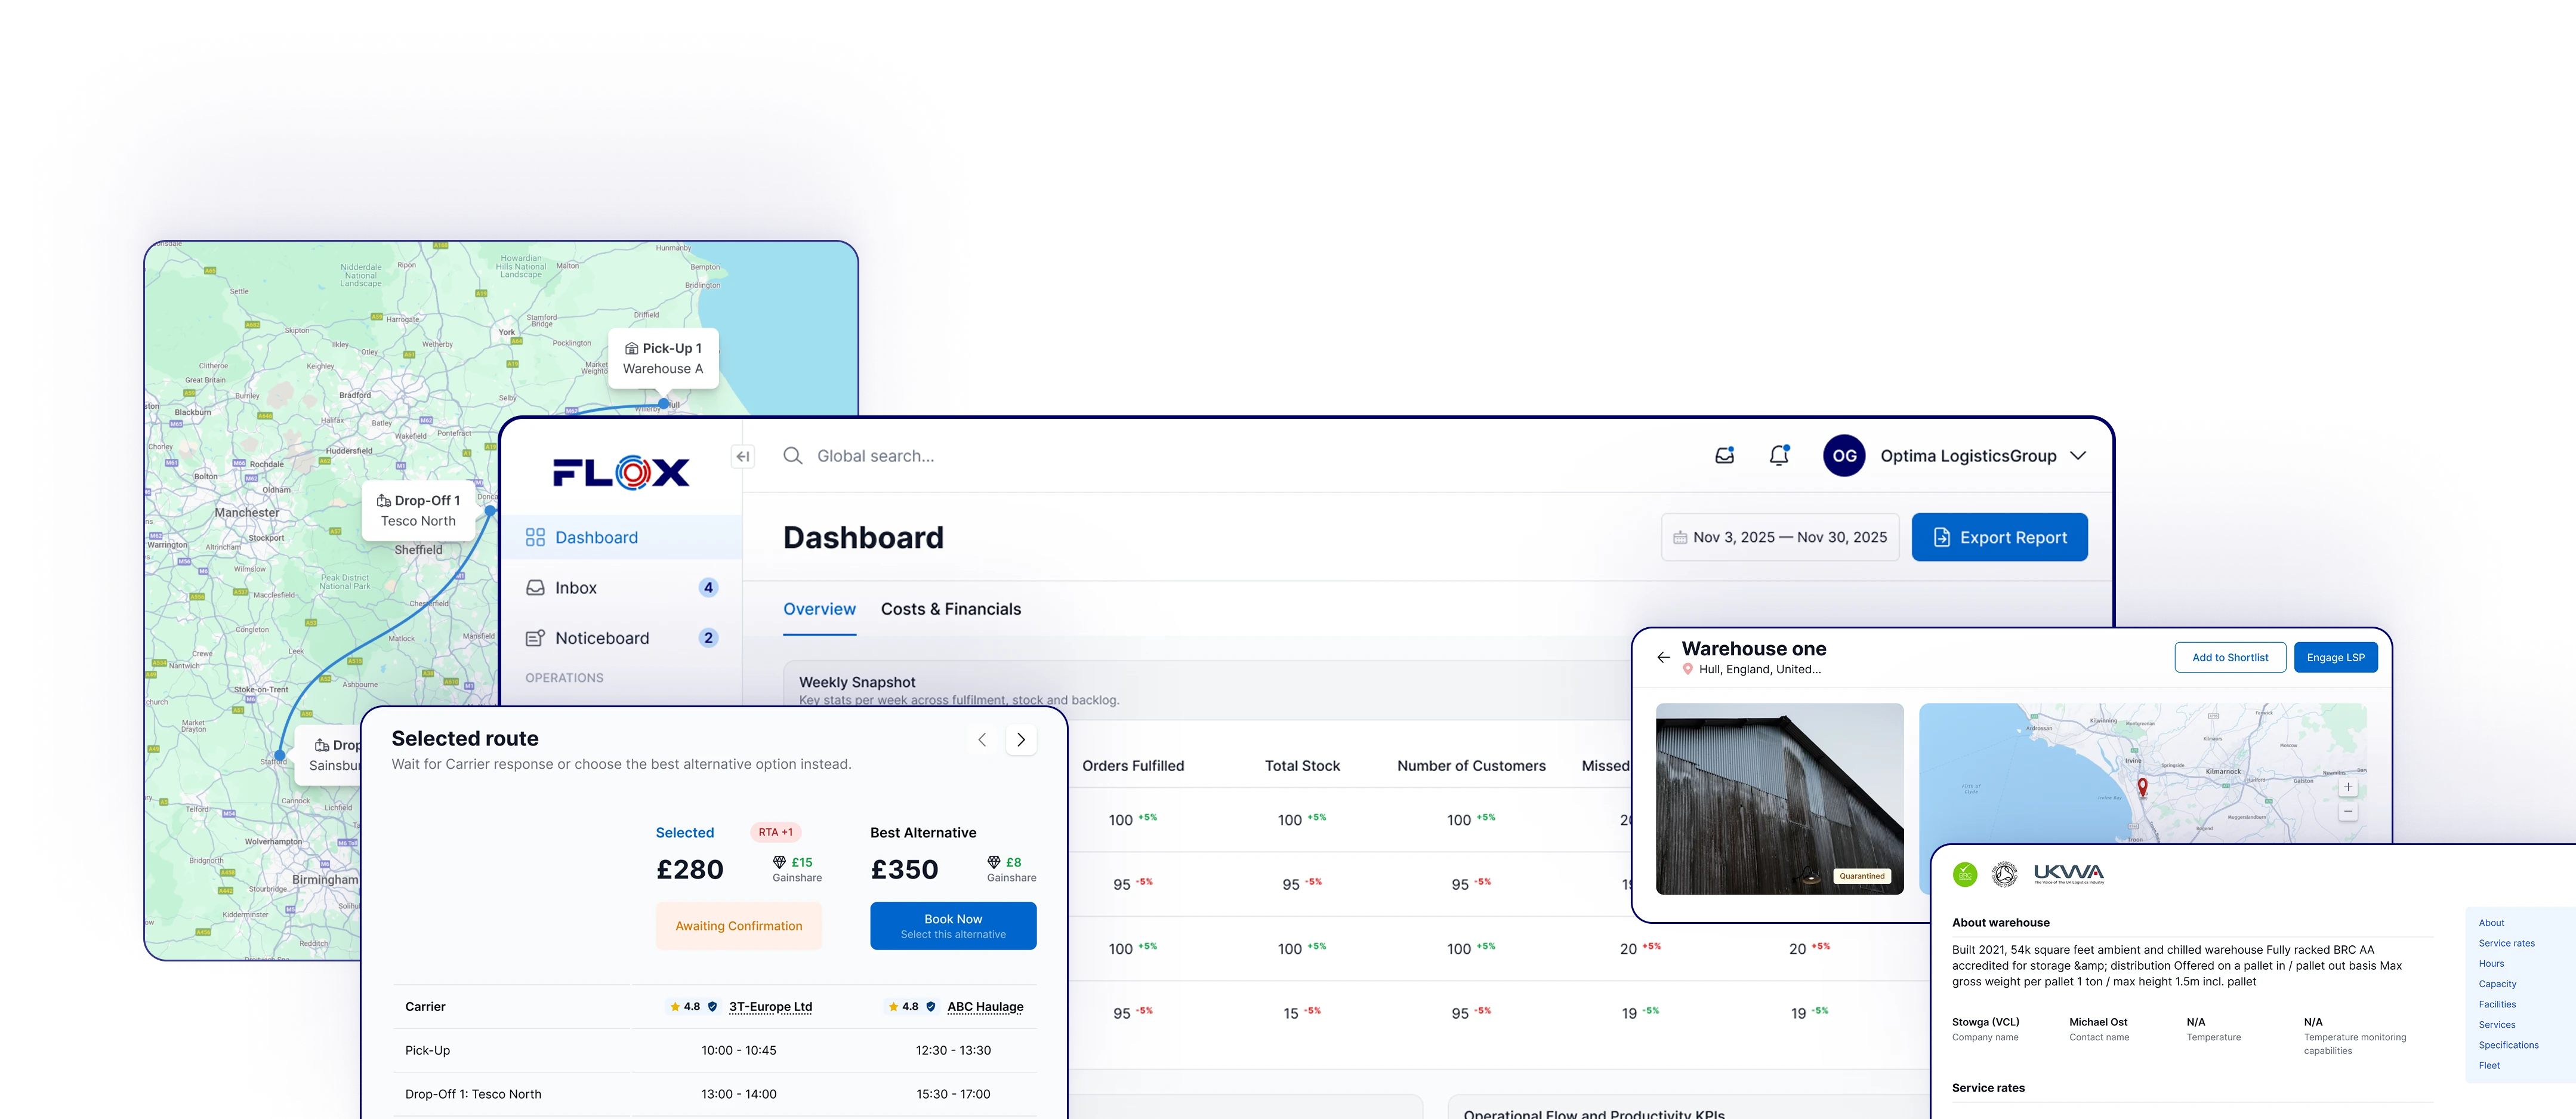


The disruption to order flow that follows a cyber incident forces every manual workaround into the open. Shippers who relied on a single integration path between their order management system and their despatch operation find that path blocked and there is no fallback. The security event is the trigger; the single point of failure was built in long before.
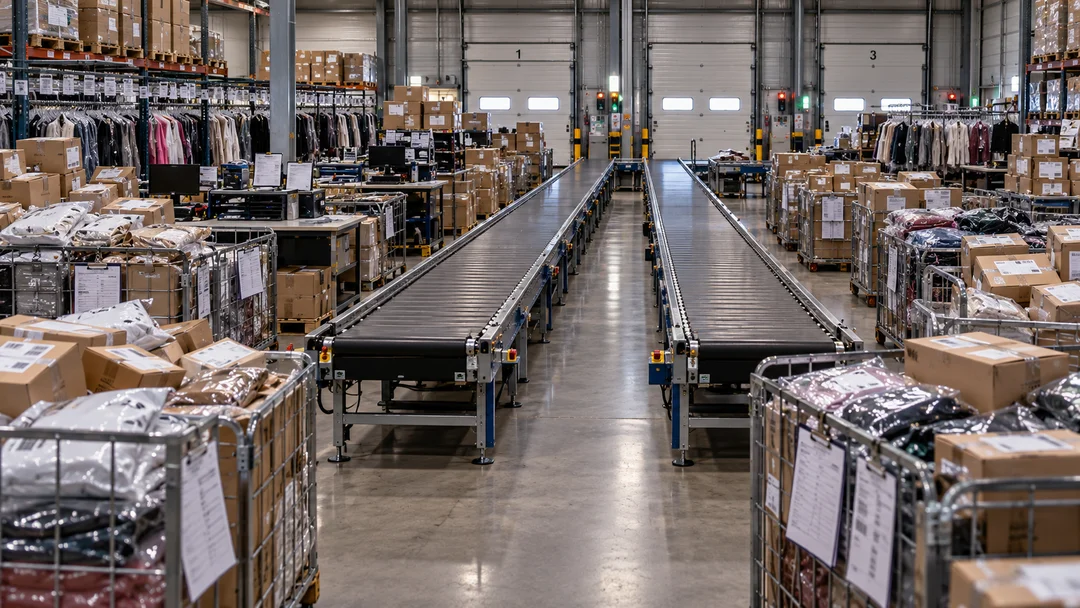
Fashion retail is a useful stress case because the order-to-despatch cycle is short and volume-sensitive. A few days of degraded throughput compounds quickly into fulfilment backlogs, carrier booking gaps and stock that cannot be committed. The operational cost lands on the warehouse and the haulier, not on the system that failed.
The practical lesson is not about cyber hygiene alone. It is about whether the coordination layer between buyer, warehouse and carrier can continue when one upstream system degrades. Most cannot, because that coordination was never made explicit. It lived in habit, in one platform's uptime or in a single ops manager's inbox.
Building redundancy into the order-to-despatch flow means mapping every handoff across each party involved, then testing what breaks when any one of those handoffs goes dark. That audit rarely happens before an incident forces it.